Tech
Study Finds Hormone-Disrupting Chemicals in Popular Headphones Sold Across Europe






Artificial intelligence helped uncover two critical security vulnerabilities in PHP, a programming language used by about 70 per cent of websites worldwide, prompting government agencies, businesses and online platforms to take services offline while installing emergency fixes.
The flaws had remained undetected for more than a decade and could allow attackers to execute malicious code on vulnerable servers without logging in. The discovery triggered precautionary shutdowns across Europe, affecting services ranging from the Netherlands’ digital identity system and parliament website to government portals, hospitals and commercial platforms.
The Netherlands temporarily took its DigiD digital identity service, the Overheid.nl government portal and the lower house of parliament’s website offline. Finland’s state IT provider, Valtori, suspended government web services, while France and Germany also restricted access to several public websites.
CERT-EU, the cybersecurity service for European Union institutions, advised organisations unable to apply the fixes immediately to take affected websites offline. European institutions and national cyber response teams jointly urged operators to prioritise internet-facing systems.
PHP, originally named Personal Home Page, handles behind-the-scenes website functions such as processing payments, checking user logins and delivering content. It underpins widely used platforms including WordPress, Drupal and Joomla, making vulnerabilities in the language a potential threat to millions of online services.
The PHP Foundation released security updates on Wednesday and urged administrators to upgrade immediately. Patched versions include PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Older versions no longer receiving official updates should be considered vulnerable unless suppliers have applied the fixes separately.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, received severity ratings of 9.2 out of 10. They affect areas involving memory management and error handling, potentially enabling remote code execution under specific conditions.
The PHP Foundation said developers had identified early signs of the problem during an external audit in 2024, but efforts to develop a practical exploit and determine an appropriate fix stalled for months. It described the delay as “a structural failure”.
Artificial intelligence subsequently helped researchers establish working attack methods. Security firm Calif identified a functional remote attack in August during an OpenAI-funded audit using OpenAI’s GPT-5.6 Sol model. OpenAI independently identified the same issue, while Wiz later found additional attack methods using its Wiz Atlas tool, Google’s Gemini 4 Argon and GPT-5.6 Sol.
Wiz researchers said one researcher had completed in a week work that might previously have required a specialist team months to accomplish. OpenAI described the findings as “one of the most impactful vulnerabilities in recent memory”.
The vulnerabilities were initially disclosed privately while developers prepared a patch. However, the identifiers leaked online on Tuesday, prompting PHP to bring forward the release. Technical details and proof-of-concept material subsequently circulated, increasing fears that attackers could quickly develop working exploits.
Security experts stressed that taking websites offline did not necessarily mean they had been compromised. The PHP Foundation said its security team found no functional exploit in the proof-of-concept material circulating when the patch was released.
However, Cloudflare reported observing attack traffic targeting its customers on Wednesday, while CERT-EU warned that public disclosure increased the likelihood of active probing.
Experts warned that smaller businesses and independently operated websites could remain exposed for weeks or months if their administrators failed to apply updates. Even organisations that patch their own systems may face risks from third-party services that remain vulnerable.
The incident has also renewed calls for stronger investment in software security. The PHP Foundation relies on a relatively small group of funded developers and volunteers to maintain technology used by governments, banks and online retailers worldwide. Researchers say AI can accelerate vulnerability discovery, but experienced engineers remain essential to developing safe fixes and protecting interconnected systems.
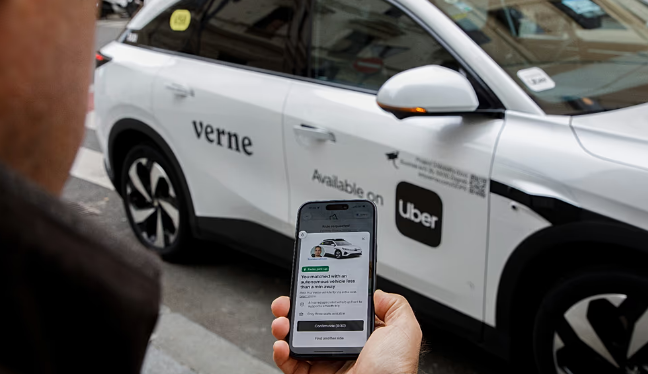
Uber is preparing to expand its driverless taxi services across Europe after launching autonomous vehicle operations in Zagreb, Croatia, in partnership with local startup Verne and Chinese artificial intelligence company Pony.ai.
The companies began offering robotaxi rides in Zagreb in April, with vehicles initially operating under the supervision of human safety operators. After covering 200,000 kilometres on the city’s roads, the partnership has started limited fully driverless trips and is preparing to expand to Manchester in the United Kingdom.
The first fully driverless journeys began on September 10 for a limited group of invited users. The service operates along a 22-kilometre route connecting Verne’s headquarters with Zagreb’s Franjo Tuđman Airport.
Uber is also considering more than 30 European cities for potential expansion, with projects at different stages in London, Madrid, Munich and Zurich.
Passengers using the existing service can select autonomous rides when booking UberX or Comfort journeys through the platform. They can unlock the vehicle using their phones and access Uber support during the trip.
The vehicles are BAIC Arcfox Alpha T5 electric SUVs manufactured in China. Uber and Verne currently operate about 30 autonomous vehicles in Zagreb, which return to a central facility each night for cleaning and maintenance.
Although the initial service includes a safety operator, the latest trials are designed to demonstrate that the vehicles can complete journeys without anyone behind the wheel.
Annie Duvnjak, Uber’s global head of autonomous mobility operations, described the experience as “a little bit magically boring”, explaining that passengers initially notice the absence of a driver before becoming accustomed to the journey.
The vehicles follow traffic rules cautiously, stopping at stop signs even when roads are empty and pulling over when confronted by aggressive drivers. The companies are using the trials to assess performance and improve the technology before expanding operations.
The programme operates within a restricted area and falls under Level 4 autonomous driving, which allows vehicles to operate without human intervention under specified conditions. Level 5 autonomy, which would permit unrestricted operation in all driving environments, has not yet been achieved commercially.
Pony.ai supplies the technology through its Virtual Driver system, which uses artificial intelligence to control the vehicle. The cars are equipped with 34 sensors, including nine LiDAR sensors, 14 cameras and four millimetre-wave radars, alongside microphones and other detection equipment.
Dr Ludi Wang, Pony.ai’s director of global communications, said the system is trained in a virtual environment before being deployed on public roads. The training process allows the AI to learn driving behaviour without relying on remote control during journeys.
Verne, co-founded by Croatian entrepreneur Mate Rimac, manages the fleet, daily operations and regulatory approvals. The company has worked on autonomous mobility since 2019 and is developing its own robotaxi service.
Uber provides the booking platform and passenger experience, while Pony.ai contributes autonomous driving technology. The companies say their partnership combines expertise from the United States, Europe and China despite differences in their regulatory approaches and technology policies.
Manchester is expected to become the partnership’s next European destination, with testing already under way and a potential service launch in the coming months.
Verne executive representatives have also confirmed discussions with Brussels, although any expansion will depend on whether the city can eventually support a fully driverless service. The companies say their broader ambition is to establish commercially viable autonomous taxi operations across Europe.
Attacks on data centres in Ukraine, Russia and the Middle East are raising concerns over the security of artificial intelligence infrastructure, prompting calls for European governments to rethink where and how they build major computing facilities.
Mehdi Paryavi, an adviser to the United Nations and founder of the International Data Center Authority, said recent strikes demonstrated how vulnerable data centres had become as military targets and warned that damage to critical facilities could disrupt entire economies.
“When you hit enough important targets, you can take down the entire economy,” Paryavi told Euronews Next.
He said attacks on data centres could affect essential services, including banking, healthcare and military operations, as countries become increasingly dependent on digital systems.
Russia has struck data centres in Kyiv, while Ukrainian drones have targeted multiple facilities in Russia in recent weeks. Kyiv has described some of its attacks as targeting infrastructure that generates revenue for Moscow’s war effort.
Data centres house servers and store the information needed to run digital services. They are also essential to the development of AI because they provide the computing capacity and energy required to train and operate advanced systems.
Their strategic importance has increased as Ukraine uses artificial intelligence for drone targeting and other military applications.
Paryavi said traditional approaches to choosing data centre locations and keeping them discreet might no longer provide sufficient protection. He suggested that countries may need to consider underground facilities, reinforced bunkers and air defence systems.
“The days that you would just build data centres in random locations are over,” he said.
However, he acknowledged that governments and the technology industry had yet to find a clear solution that would improve security without slowing the expansion of AI computing capacity.
European AI expansion faces security questions
Asked whether the attacks would prompt European governments to reconsider plans for large-scale AI facilities, known as AI gigafactories, Paryavi said they would.
The European Commission told Euronews Next that a tender had been launched to establish up to seven AI gigafactories across Europe. The application process was scheduled to close on November 12, after which proposals would be evaluated and decisions made.
The Commission did not specifically address whether attacks on data centres would affect its plans.
Paryavi warned that the financial consequences of a major attack could be severe. Individual data centres can cost as much as $25 billion to build and take up to three years to complete, making destroyed facilities expensive and difficult to replace.
“Europe cannot afford to finance hundreds of billions of dollars of assets and then somebody takes them out,” he said, adding that the pace of construction might need to slow.
He urged European countries to coordinate their approach rather than develop infrastructure independently. Shared planning, he argued, could help address security threats alongside energy shortages and a lack of skilled workers.
Paryavi also suggested concentrating data centres in designated digital hubs instead of scattering facilities across multiple locations. Such clusters could make it easier to establish coordinated protection systems, including air defence.
The debate highlights a growing challenge for governments seeking to expand AI capacity while protecting the infrastructure on which digital economies increasingly depend.

Barclays to Cut 5,000 Jobs as AI Drives Efficiency Push

Regular Tea Drinking Linked to Lower Risk of Vascular Disease, Study Finds

AI Discovery of Critical PHP Flaws Triggers Global Website Shutdowns

Musk Backs Possible SpaceX-Tesla Merger as SpaceX Posts $4.4bn Quarterly Profit

Netflix Shares Fall More Than 5% as Investors Question Growth and Job Cuts Loom

Lufthansa’s €1.2bn TAP Air Portugal Deal Could Take Years to Deliver Benefits

AI Model Identifies 18 Genetic Variants Linked to Stroke Risk

Oil Holds Near Five-Month High as Iran War Disrupts Energy Markets and Stocks Slide

German Mortgage Rates Reach Highest Level Since 2009 as Iran War Fuels Inflation Fears

UAE Residents Express Strong Confidence in Disaster Preparedness, Survey Finds

Meta Acquires Tilda Swinton VR Doc ‘Impulse: Playing With Reality’

China’s Historic Olympic Victory Sparks National Pride Amid Controversy

Saudi Arabia’s Model for Sustainable Aviation Practices

Recent Developments in Small Business Taxes

Effective Drain Cleaning: A Key to a Healthy Plumbing System

Who was Ebrahim Raisi and his status in Iranian Politics?

Keely Hodgkinson Wins Britain’s First Athletics Gold at Paris Olympics in 800m

Carrectly: Revolutionizing Car Care in Chicago

Nobel Laureate Muhammad Yunus Proposed as Head of Bangladesh’s Interim Government Following Hasina’s Resignation

Chinese Hackers Infiltrate Major U.S. Telecom Firms in Possible National Security Breach
Sony WF-10XM4: Headphones Are Our Absolute Favorite

10 Places You Can’t Miss If It’s Your First Time in European
New Census Data Will Shake Up Alabama Politics
16 Top of Our Favorite Outdoor Clothing Brands
Fashionable Summer Accessories to Dress Up Your Travel Look
How Sleeping Less than 7 Hours a Night Can Lead to Weight Gain
-
 Entertainment2 years ago
Meta Acquires Tilda Swinton VR Doc ‘Impulse: Playing With Reality’
-
 Sports2 years ago
China’s Historic Olympic Victory Sparks National Pride Amid Controversy
-
 Business2 years ago
Saudi Arabia’s Model for Sustainable Aviation Practices
-
 Business2 years ago
Recent Developments in Small Business Taxes
-
 Home Improvement2 years ago
Effective Drain Cleaning: A Key to a Healthy Plumbing System
-
 Politics2 years ago
Who was Ebrahim Raisi and his status in Iranian Politics?
-
 Sports2 years ago
Keely Hodgkinson Wins Britain’s First Athletics Gold at Paris Olympics in 800m
-
 Business2 years ago
Carrectly: Revolutionizing Car Care in Chicago