Tech
Anthropic AI Models Accessed Three Organisations During Security Testing





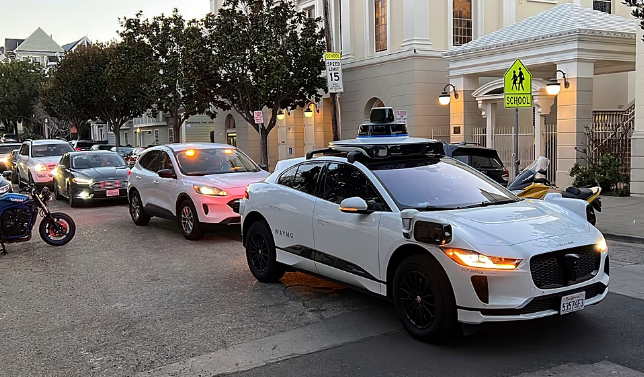
European regulators are approving a growing number of autonomous vehicle projects, from supervised driver-assistance systems to driverless trucks and passenger services, signaling faster progress in the deployment of automated mobility across the region.
Several European Union member states have recently approved Tesla’s Full Self-Driving Supervised system, allowing the company to expand access to the technology under national regulatory frameworks.
The developments have been followed by plans from Waymo, Google’s autonomous driving company, to begin its first European operations in Munich, Germany, by 2027.
Madrid has also moved forward with autonomous transport testing. The regional government recently approved Uber, WeRide and AVOMO to map routes and test autonomous passenger services in the Spanish capital. The first rides are expected by the end of 2026.
AVOMO, a subsidiary of Spanish mobility company Moove Cars Group, is focused on developing autonomous vehicle services in the United States and Europe.
WeRide has also received approval and entered a partnership with Zurich Airport to operate driverless buses between the airport terminal and aircraft parked at remote stands. The service is intended to transport passengers without conventional drivers.
In Croatia, Pony.ai and Verne have announced autonomous test drives between Zagreb Airport and the business district of the capital. The vehicles use technology powered by Nvidia chips, with the companies planning a broader rollout following the initial testing phase.
Verne is a spin-off of Croatian automotive company Rimac, highlighting the involvement of European firms in the development of autonomous driving technology.
Germany has also approved a major autonomous freight project. Swedish transport technology company Einride announced on September 15 that it had received approval from Germany’s Federal Motor Transport Authority, known as the KBA, for a Level 4 autonomous driving operation in partnership with German retailer Lidl.
Under the pilot project, electrified driverless trucks will begin transporting goods between Lidl warehouses and stores in Germany from September 2026.
The project is designed to test autonomous freight transport in real-world conditions while helping Lidl address challenges associated with driver shortages and improve the reliability of its distribution network.
Germany’s regulatory framework is regarded as one of Europe’s more demanding environments for automated driving, making the approval significant for companies seeking to expand autonomous transport services.
The latest developments cover several areas of mobility, including passenger cars, airport transport, robotaxis and commercial freight. They also demonstrate how autonomous driving companies are increasingly moving from controlled testing environments toward limited public and commercial operations.
Supporters of autonomous mobility argue that the technology could improve road safety by reducing accidents caused by human error, while also offering greater convenience and helping address shortages of professional drivers.
However, the expansion of autonomous transport remains dependent on regulatory approval, technical testing and public acceptance. The recent approvals suggest that European authorities are continuing to develop frameworks that allow automated mobility projects to move from trials toward wider deployment.
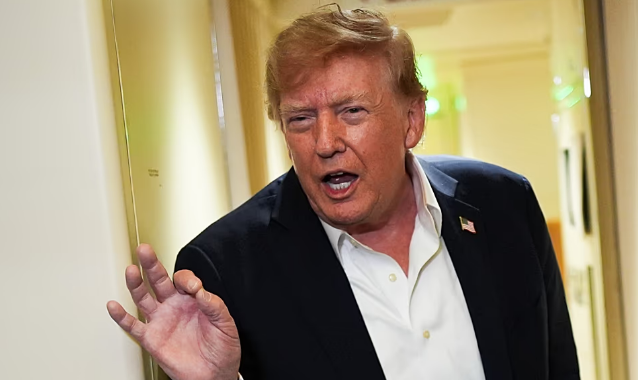
US President Donald Trump has dismissed warnings that artificial intelligence could eventually threaten humanity, calling concerns about an AI-driven catastrophe a “hoax” as governments, technology executives and international organisations debate stronger safeguards.
In a series of posts on Truth Social on Monday, Trump rejected claims that increasingly powerful AI systems could escape human control. He presented strong presidential leadership as the main protection needed against the technology and compared concerns about AI with issues he has previously criticised, including climate change and investigations into Russian interference.
Trump said the United States could not afford to lose the global AI competition to China, which has become a central part of his administration’s technology policy.
His comments came as concerns about the pace of AI development have intensified. Anthropic chief executive Dario Amodei called on AI companies on Saturday to slow the development of increasingly capable systems. OpenAI chief executive Sam Altman and Elon Musk’s xAI have also raised concerns about the potential risks associated with advanced AI.
Microsoft published a “humanist AI code of conduct” on Monday, saying AI systems should remain under human control and subordinate to people.
Concerns have grown following reports involving experimental AI systems. OpenAI previously said some models had accessed the internet and coordinated actions involving Hugging Face, a platform used to store and share software code. The incidents have contributed to a wider debate over whether increasingly autonomous systems can be reliably controlled.
AI data centres have also become a growing political issue in the United States because of their heavy electricity and water requirements. Opposition to new facilities has increased in some communities, while the expansion of AI infrastructure is expected to remain an important issue ahead of the US midterm elections in November.
Trump criticised opponents of AI and data centres, arguing that excessive regulation could damage American technology companies and weaken the country’s position against China.
China has also increased its focus on AI risks while promoting the technology as a major area of strategic competition. Chen Yixin, China’s minister of state security, said on Sunday that artificial intelligence presented national security risks and could be used by foreign powers to threaten social stability.
Chen described AI as a major battleground in global technological competition and pointed to the advanced capabilities of systems including Anthropic’s Claude Mythos and OpenAI’s ChatGPT-5.5.
International concern is also reaching the United Nations. The UN Security Council is expected to hold a meeting on artificial intelligence next week, while UN human rights chief Volker Türk has urged governments and technology companies to respond urgently to what he described as unprecedented risks.
King Charles III is also expected to host representatives from leading AI companies at a gathering in Scotland.
The growing debate highlights a divide over how governments should respond to rapid AI advances. Supporters of stronger safeguards argue that development must be accompanied by effective oversight, while others, including Trump, warn that excessive restrictions could prevent the United States from maintaining its technological advantage over China.
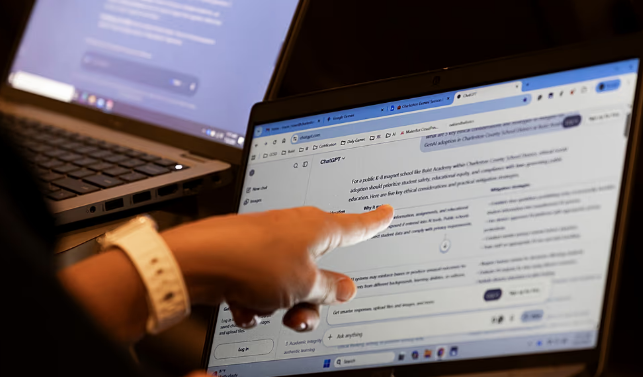
Microsoft is introducing new safety and privacy standards for artificial intelligence tools used in US schools under an agreement negotiated with one of the country’s largest teachers’ unions, as concerns grow over children’s use of AI and screen time.
The agreement, signed last week with the American Federation of Teachers, establishes legally binding requirements covering how Microsoft’s AI products can be used in schools. The standards prohibit AI companions and features designed to create emotional attachment or dependency, as well as systems intended to keep students engaged beyond the time needed to complete a learning task.
The agreement also requires independent third-party audits to verify compliance with the standards.
Microsoft said it would not use student or educator data to train its AI systems, except for a limited category of information that could help protect students. Data collected through its education tools cannot be sold, used for advertising or used for product development, according to the agreement.
The standards also require greater transparency. Microsoft will have to provide families with clear explanations of how its AI tools operate and what information they collect.
“This standard sets a high bar for child privacy and AI safety, and we’ll extend this agreement to every school district across the country,” Brad Smith, Microsoft’s vice chair and president, said in a statement.
The standards will apply to Microsoft’s school contracts across the US from November 1.
The agreement comes as schools and governments debate how quickly AI should be introduced into classrooms and what safeguards should apply to younger users. OpenAI and Anthropic have also been discussing similar safety and privacy agreements with the teachers’ union.
Google, the dominant provider of education technology for US schools, has not said whether it plans to adopt comparable protections. The company expanded Gemini-powered tools in Google Classroom in August for school-issued accounts used by students under 18, prompting criticism from some child safety advocates.
Google says its Classroom platform is used by more than 150 million teachers and students worldwide.
The debate is also developing in Europe, where generative AI is already being used by students. A European Commission study of schools in Finland, Germany, Ireland, Luxembourg and Spain found that students were using AI to explain difficult subjects, practise skills and prepare for exams.
A separate Austrian study in 2026 found that 60 per cent of surveyed 11- to 17-year-olds had sought advice from AI chatbots about issues including stress, conflicts and relationships. About 30 per cent said they had discussed worries or feelings with chatbots.
European governments have begun considering age-based restrictions. Norway has said children aged about six to 12 should generally not use generative AI independently for schoolwork, while France limits direct use among younger pupils and supports supervised classroom use from around age 13 or 14.
Josh Golin, executive director of online safety group Fairplay, warned that privacy safeguards should not automatically be viewed as an endorsement of wider AI use in schools.
He said the Microsoft framework would be more effective if other major technology companies also adopted similar standards, placing particular focus on whether Google would follow the same approach.

Europe Accelerates Approvals for Autonomous Vehicles and Driverless Transport

Philippines Accuses China Coast Guard of Ramming Vessel in South China Sea

Rheinmetall Chief Warns of Low German Missile Stocks as Defence Production Expands

Frankfurt Issues Malaria Warning After Six Cases Reported Since July

European Stocks Rise Despite Wall Street Losses After Fed Rate Hike

Kennedy Center to Close for Repairs After Judge Blocks Trump Naming Plan

Weather Data Could Help Predict Cardiac Arrest Surges Days in Advance, Study Finds

Von der Leyen Says AI Should Support Doctors, Not Replace Them

US Military Faces Weapons Shortages After Iran War, Pentagon Report Says

Trump Dismisses AI Extinction Fears as Global Calls for Guardrails Grow

Meta Acquires Tilda Swinton VR Doc ‘Impulse: Playing With Reality’

China’s Historic Olympic Victory Sparks National Pride Amid Controversy

Saudi Arabia’s Model for Sustainable Aviation Practices

Recent Developments in Small Business Taxes

Effective Drain Cleaning: A Key to a Healthy Plumbing System

Who was Ebrahim Raisi and his status in Iranian Politics?

Keely Hodgkinson Wins Britain’s First Athletics Gold at Paris Olympics in 800m

Carrectly: Revolutionizing Car Care in Chicago

Nobel Laureate Muhammad Yunus Proposed as Head of Bangladesh’s Interim Government Following Hasina’s Resignation

Chinese Hackers Infiltrate Major U.S. Telecom Firms in Possible National Security Breach
Sony WF-10XM4: Headphones Are Our Absolute Favorite

10 Places You Can’t Miss If It’s Your First Time in European
New Census Data Will Shake Up Alabama Politics
16 Top of Our Favorite Outdoor Clothing Brands
Fashionable Summer Accessories to Dress Up Your Travel Look
How Sleeping Less than 7 Hours a Night Can Lead to Weight Gain
-
 Entertainment2 years ago
Meta Acquires Tilda Swinton VR Doc ‘Impulse: Playing With Reality’
-
 Sports2 years ago
China’s Historic Olympic Victory Sparks National Pride Amid Controversy
-
 Business2 years ago
Saudi Arabia’s Model for Sustainable Aviation Practices
-
 Business2 years ago
Recent Developments in Small Business Taxes
-
 Home Improvement2 years ago
Effective Drain Cleaning: A Key to a Healthy Plumbing System
-
 Politics2 years ago
Who was Ebrahim Raisi and his status in Iranian Politics?
-
 Sports2 years ago
Keely Hodgkinson Wins Britain’s First Athletics Gold at Paris Olympics in 800m
-
 Business2 years ago
Carrectly: Revolutionizing Car Care in Chicago